
Introduction to TheJavaSea.me Leaks AIO-TLP371
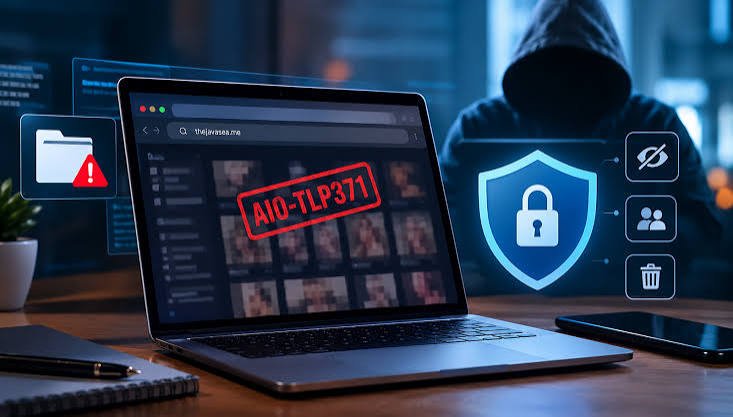
The keyword thejavasea.me leaks aio-tlp371 has attracted attention among internet users interested in leaked files, online security, and digital privacy. When unfamiliar website names appear alongside terms such as “leaks” and a technical identifier like “AIO-TLP371,” it is natural to wonder what the material refers to, why people are discussing it, and whether accessing it could create security risks.
However, it is important to distinguish between verified information and speculation. The name AIO-TLP371 alone does not establish what a file contains, who created it, or whether it is connected to a genuine security incident. Without reliable documentation, claims about its contents should not be treated as confirmed facts.
The term “leaks” generally describes information or files that have been shared without the permission of their owner. Depending on the circumstances, leaked material may include private documents, software packages, account information, source code, or other digital content. Some leaks involve legitimate public-interest disclosures, while others expose personal information or distribute copyrighted material without authorization.
This article explores the meaning of the keyword, the possible security concerns associated with leaked files, and the precautions users can take when encountering unfamiliar online downloads. The goal is to provide a practical, balanced explanation without presenting unverified claims about AIO-TLP371 as established facts.
What Is TheJavaSea.me?
TheJavaSea.me is the website name associated with the keyword under discussion. To understand its relevance, users should first consider the difference between a website’s name, the content hosted on it, and the claims people make about that content elsewhere online.
A domain name does not automatically reveal whether a website is trustworthy. A site may publish ordinary informational content, host downloadable files, link to third-party resources, or change its purpose over time. Consequently, judging a website solely by its name or by a search result can lead to inaccurate conclusions.
When a website is associated with leaked material, it becomes particularly important to examine the available evidence carefully. Users should look for credible reporting, clear ownership information, transparent policies, and independent security assessments rather than relying exclusively on anonymous posts or promotional descriptions.
It is also worth remembering that a website’s apparent popularity does not guarantee that its files are safe. Downloads may be hosted by external services, and a page may contain misleading buttons, deceptive advertisements, or links that redirect visitors to unrelated destinations. A careful approach helps users avoid unnecessary exposure to these risks.
Understanding the AIO-TLP371 Keyword
AIO-TLP371 appears in the search phrase as a specific identifier associated with the alleged leak. Nevertheless, the identifier by itself does not provide enough information to determine whether it represents a software package, an archive, a collection of files, or something entirely different.
Technical labels are often used to distinguish versions, releases, collections, and individual resources. Some are created by developers, while others are assigned by TheJavaSea.me Leaks AIO-TLP371 uploaders or online communities. Without a reliable source explaining the identifier, it would be misleading to assign a precise meaning to AIO-TLP371.
The word “AIO” is sometimes used as an abbreviation for “all-in-one” in technology-related contexts. Even so, that common usage does not prove that this particular identifier describes an all-in-one software package. Context matters, and assumptions based on familiar abbreviations can create confusion.
For readers researching the keyword, the best approach is to look for documentation from a verifiable source. A trustworthy explanation should identify the material, explain its origin, and distinguish confirmed details from allegations. If those elements are missing, it is better to acknowledge the uncertainty than to repeat unsupported claims.
Potential Risks of Downloading Leaked Files
Downloading unknown files can expose a device to several forms of cybersecurity risk. One common concern is malware, which includes malicious programs designed to steal information, disrupt systems, monitor activity, or provide unauthorized access to a computer.
A file may appear harmless while containing hidden executable content or instructions that trigger dangerous behavior. Attackers sometimes disguise malicious files as documents, software installers, archives, or useful utilities. File names and attractive descriptions are not reliable indicators of safety.
Another risk involves credential theft. A deceptive download page may ask visitors to sign in, complete a verification process, or provide personal details before accessing a file. Such requests can be used to collect passwords, email addresses, payment information, or other sensitive data. Users should avoid entering credentials into unfamiliar websites.
Privacy exposure is another concern. Some files may contain information belonging to individuals or organizations that never intended to make it public. Downloading, copying, or redistributing such material can increase the harm caused by an unauthorized disclosure. Before interacting with suspicious content, users should consider both their own security and the privacy rights of others.
How to Recognize Suspicious Websites and Downloads
One of the most useful online safety skills is recognizing warning signs before opening a download. A website that makes extraordinary promises, pressures visitors to act immediately, or claims that a file is available only through a suspicious redirect deserves additional scrutiny.
Unexpected download prompts are another warning sign. A page may display several buttons that look identical even though they lead to different destinations. Some may open advertising pages, request browser notifications, or initiate downloads that have nothing to do with the resource described.
Users should also be cautious when a website asks them to disable antivirus protection, ignore browser warnings, or install an unknown extension. Legitimate software should not require users to abandon basic security protections without a clear and verifiable technical reason.
Finally, check whether independent sources SpiritualHubz.com USA support the website’s claims. Search for credible security reports, established discussions, and official documentation. Be careful with copied articles that repeat the same unsupported statements. Multiple pages repeating one rumor do not necessarily provide independent confirmation.